Protect Your Plant.
Not Just Your Perimeter.
Full OT visibility. Behavioral threat detection. Audit-ready compliance. Zero impact on production.
Industrial-Grade OT IDS & CPS IDS Detection
Most security tools were built for IT networks. NETRUDER was built for OT and cyber-physical systems.
Deep OT protocol support gives your team full visibility across every device, connection, and event in your industrial and cyber-physical environment.
OT Protocol Intelligence
Deep packet inspection for Modbus, DNP3, IEC 104, and 30+ industrial protocols
AI-Assisted Anomaly Detection
Machine learning models trained on industrial behavior patterns
Multi-Threaded Suricata Engine
High-performance packet processing with zero network disruption
Passive Asset Fingerprinting
Protocol-level device identification with 98.5% classification accuracy across 40+ OT device families — zero packets sent
Centralized Rule Management
Unified policy orchestration across distributed sensor networks
Alert Correlation & Enrichment
Context-aware threat intelligence with automated incident linking
Trusted by critical infrastructure operators worldwide
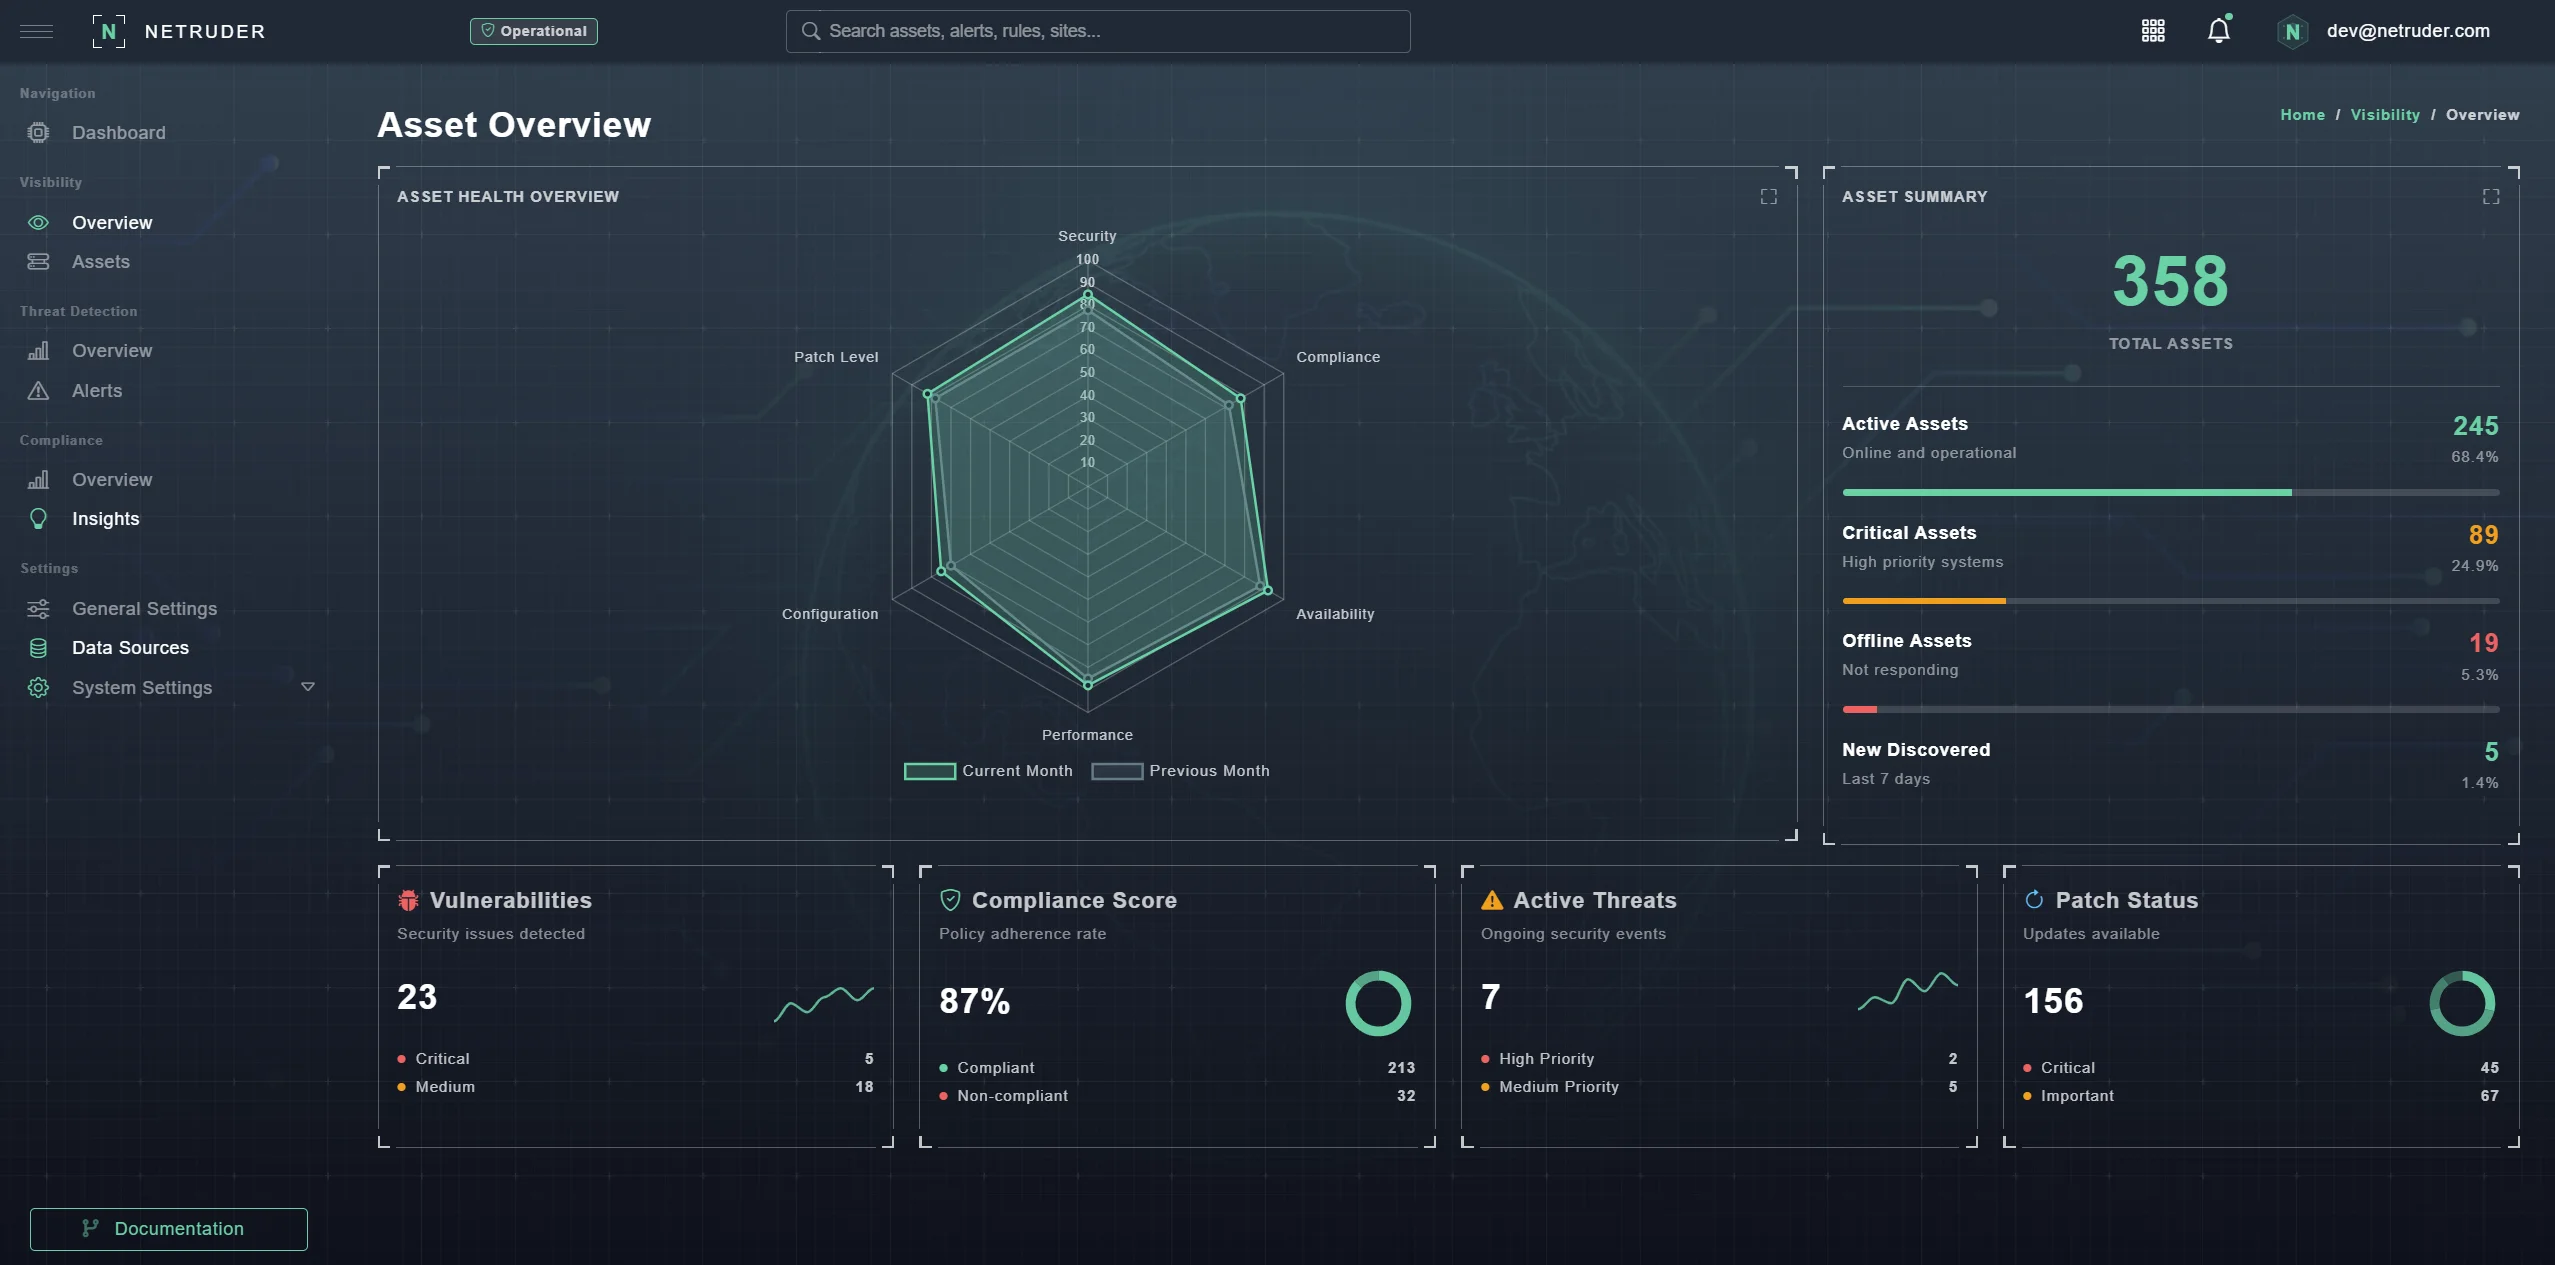
Continuous Insight Across Every Asset and Connection
See every device on your network — not just IT assets. NETRUDER automatically discovers, classifies, and monitors all OT equipment from day one, with no manual configuration required.
Protocol-level device fingerprinting with 98.5% classification accuracy across 40+ OT device families
Automated Purdue level assignment based on traffic behavior analysis
Real-time network topology mapping with vendor, model, and firmware identification
Federated sensor architecture for distributed monitoring at scale
CVE correlation engine matching fingerprinted assets against ICS-CERT and vendor advisories
Historical traffic analysis for forensic investigation and compliance
Integrated Compliance Standards
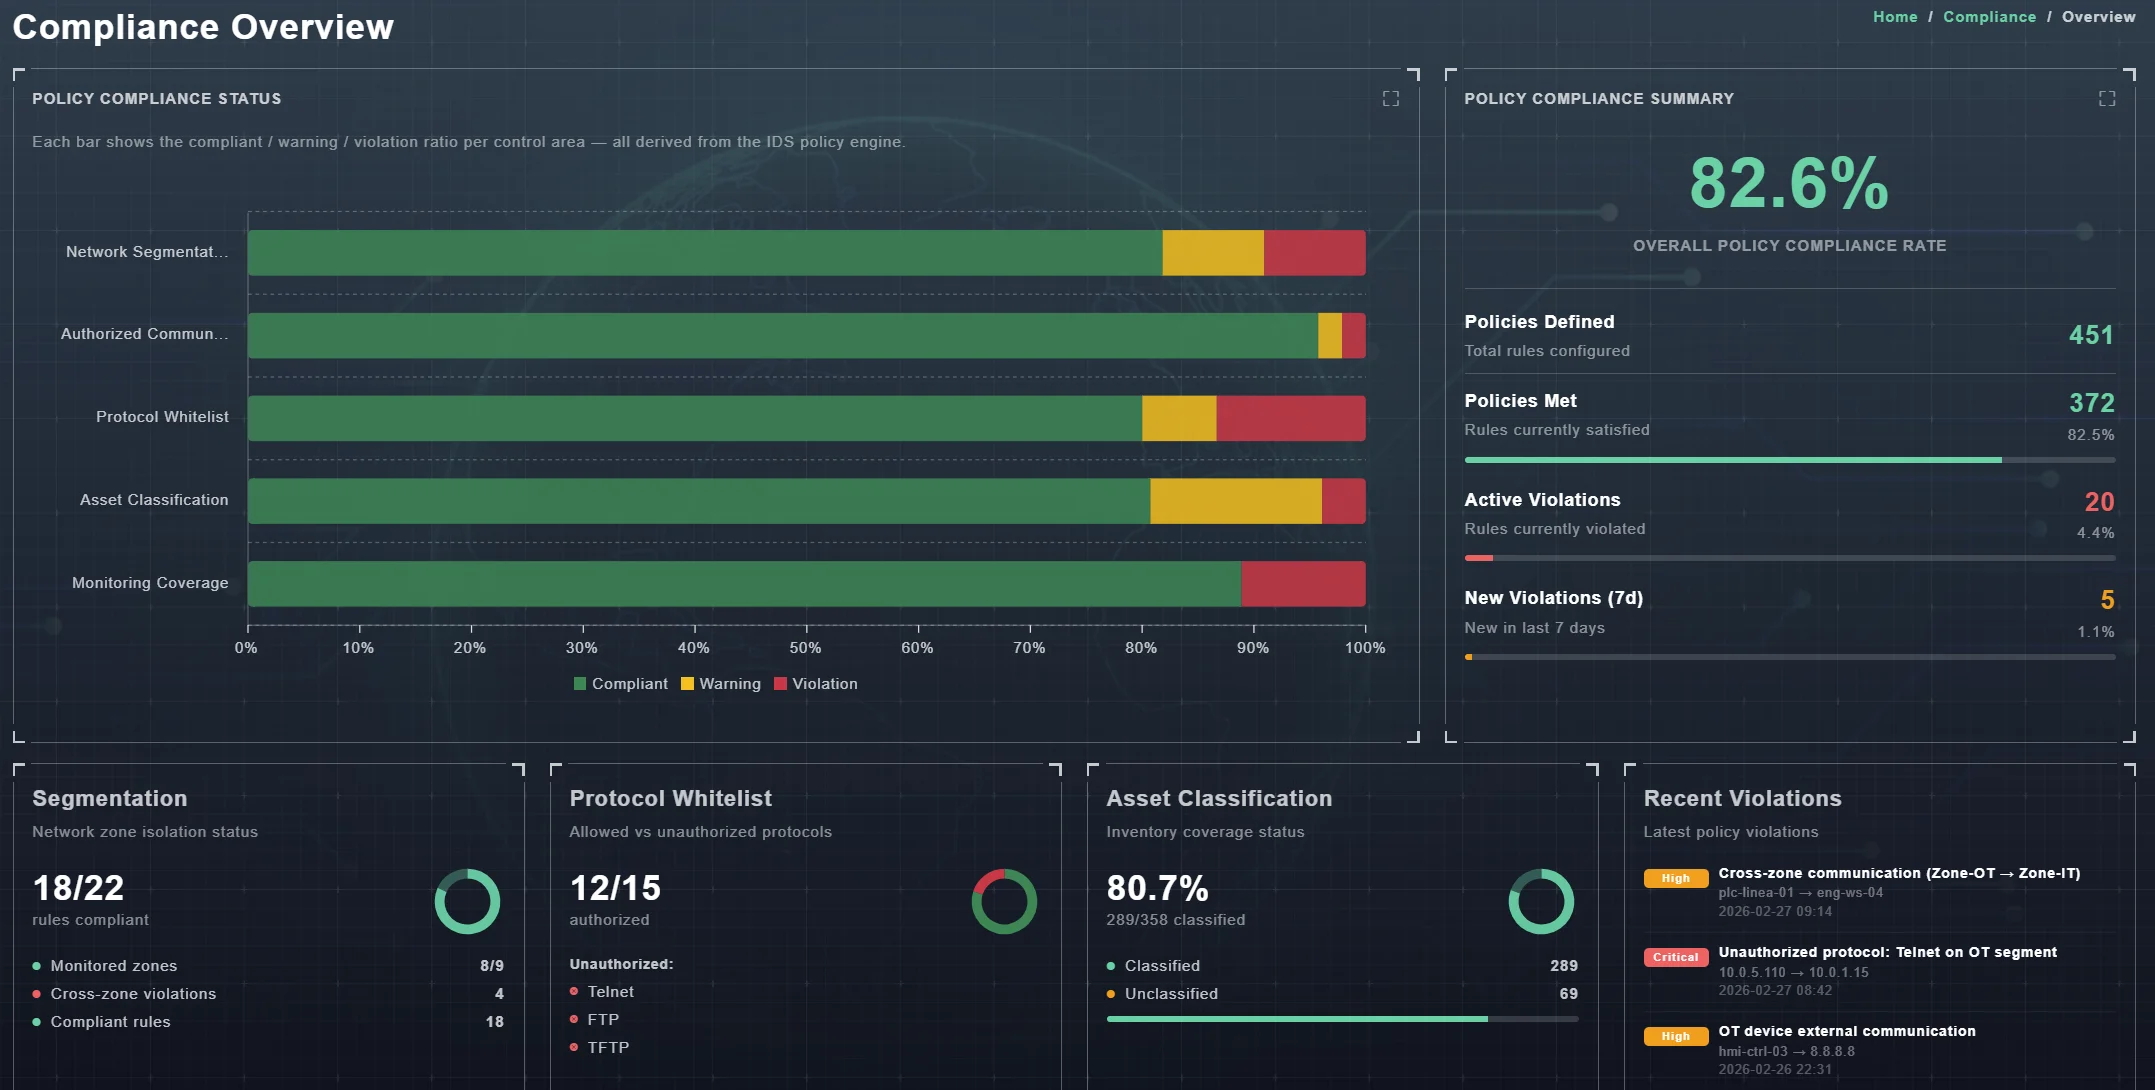
Audit-Ready Compliance, Not Just Framework Logos
NETRUDER delivers a complete GRC workflow — from automated evidence collection to audit-ready report generation. Control-level mapping shows exactly which IEC 62443, NIST 800-82, NERC CIP, and NIS2 requirements are satisfied and which have gaps.
Continuous compliance posture scoring with drift detection and automated re-assessment
Control-level mapping showing specific IEC 62443 zones/conduits and NIST 800-82 controls satisfied vs. gaps
Automated evidence collection: asset inventories, access logs, configuration snapshots, alert histories
Audit-ready export in PDF reports, CSV evidence packs, and SIEM-compatible log formats
Gap analysis with remediation tracking, owner assignment, and progress monitoring
Multi-framework support: IEC 62443, NIST 800-82, NERC CIP, NIS2, ISO 27019, EPDK
Built for Industrial Resilience
NETRUDER monitors your network passively via SPAN ports — no latency, no risk, no changes to existing infrastructure. Your operations stay running even when threats are detected.
Passive network monitoring with zero operational disruption or latency
AI-driven alert correlation reducing false positives by 85%
Adaptive response protocols aligned with operational safety requirements
Autonomous node recovery maintaining detection during network disruptions
Incident playbooks customized for industrial environments
Validated Across Critical Sectors
Real deployment outcomes from operators running NETRUDER in production environments across energy, manufacturing, water, and transportation
Energy & Utilities
European TSO deployment
Manufacturing
Global automotive OEM
Water & Wastewater
Regional water authority
Transportation
National rail operator
Security Testing & Validation
Detection capabilities aligned with MITRE ATT&CK for ICS framework. Tested against real-world OT attack techniques including unauthorized command injection, protocol manipulation, and network reconnaissance.
Performance Verified
Lab-validated performance benchmarks ensure NETRUDER meets the throughput and latency requirements of high-bandwidth industrial environments.
Fingerprinting Accuracy
Multi-layered passive identification pipeline combining protocol analysis, network heuristics, and application metadata for precise OT asset classification.
Latest Insights
Expert perspectives on industrial cybersecurity and operational resilience
Stay informed with research, case studies, and best practices from the frontlines of OT security
Why We Chose Suricata Over Snort as Our IDS Engine
A rigorous technical evaluation of Suricata versus Snort for high-throughput network intrusion detection — and why Suricata won.
How OT Threats Evolve in 2025
Emerging attack vectors targeting industrial control systems and what defenders need to know.
Building a Resilient Energy Infrastructure
Strategic approaches to protecting critical energy systems from sophisticated cyber threats.
Common Questions About NETRUDER
Get answers to the most common questions about our OT security platform
An OT IDS (Operational Technology Intrusion Detection System) is purpose-built to monitor and protect industrial control networks — SCADA, DCS, PLCs, RTUs — rather than IT environments. Unlike traditional IDS, an OT IDS understands industrial protocols (Modbus, DNP3, IEC 104), never injects packets into live control systems, and detects threats in the context of physical processes. NETRUDER is an OT-native IDS that adds zero latency to your operations.
A CPS IDS (Cyber-Physical Systems Intrusion Detection System) monitors the intersection of digital networks and physical processes — power grids, water treatment, manufacturing lines, and transportation networks. CPS environments require specialized detection because attacks don't just cause data breaches; they can cause physical harm, production downtime, or safety incidents. NETRUDER is a CPS IDS that correlates network anomalies with physical process context to deliver accurate, actionable alerts.
NETRUDER is built specifically for OT environments, not adapted from IT tools. Three key differences: native protocol support for Modbus, DNP3, and IEC 104; passive monitoring that adds zero latency to your control systems; and detection rules pre-mapped to IEC 62443 and NIST 800-82.
No. NETRUDER observes traffic passively via SPAN ports — it never injects packets or interacts with your control systems. Deployment requires no changes to existing infrastructure and adds zero latency.
Most deployments complete in 2–4 weeks. That covers sensor installation, network discovery, baseline learning, and policy tuning. Our engineers work alongside yours to keep disruption minimal throughout.
NETRUDER supports 30+ industrial protocols, including Modbus TCP/RTU, DNP3, IEC 60870-5-104, BACnet, PROFINET, EtherNet/IP, OPC UA, and S7comm. We add new protocol support regularly based on customer environments.
Yes. NETRUDER provides standardized integrations with major SIEM platforms including Splunk, QRadar, ArcSight, and Sentinel. We support syslog, REST APIs, and custom connectors to fit your security operations workflow.
NETRUDER supports IEC 62443, NIST 800-82, ISO 27019, NERC CIP, NIS2, and EPDK. Alerts and events map automatically to each framework. Built-in audit trails and policy gap reports are ready to export at any time.
NETRUDER learns what normal looks like in your specific environment during an initial baseline period. After that, it monitors continuously and flags deviations — whether from a security incident, a misconfiguration, or an unexpected operational change.
We provide 24/7 support with dedicated security engineers on call for incident response. Support covers deployment, policy tuning, threat hunting, and regular platform updates with new detection rules and protocol coverage.
NETRUDER correlates passively fingerprinted asset data against ICS-CERT, NVD, and vendor-specific advisories in real time. Each CVE match is enriched with OT context including Purdue level, process criticality, network reachability, and compensating controls to produce prioritized risk scores.
NETRUDER achieves 98.5% device classification accuracy across 40+ OT device families using protocol behavioral analysis, network traffic heuristics, and application-layer metadata extraction — all without sending a single packet.
Get in Touch
Ready to secure your industrial infrastructure? Let's discuss how NETRUDER can protect your operations.
Request a Demo
Connect
LinkedIn - NETRUDERWhy Choose NETRUDER?
- OT-native architecture
- Behavioral threat detection
- Zero operational impact
- 24/7 monitoring & support